Apache's TLS hardening follows the same principles as Nginx's, with different specific directives, typically set in the SSL module configuration or a VirtualHost block.
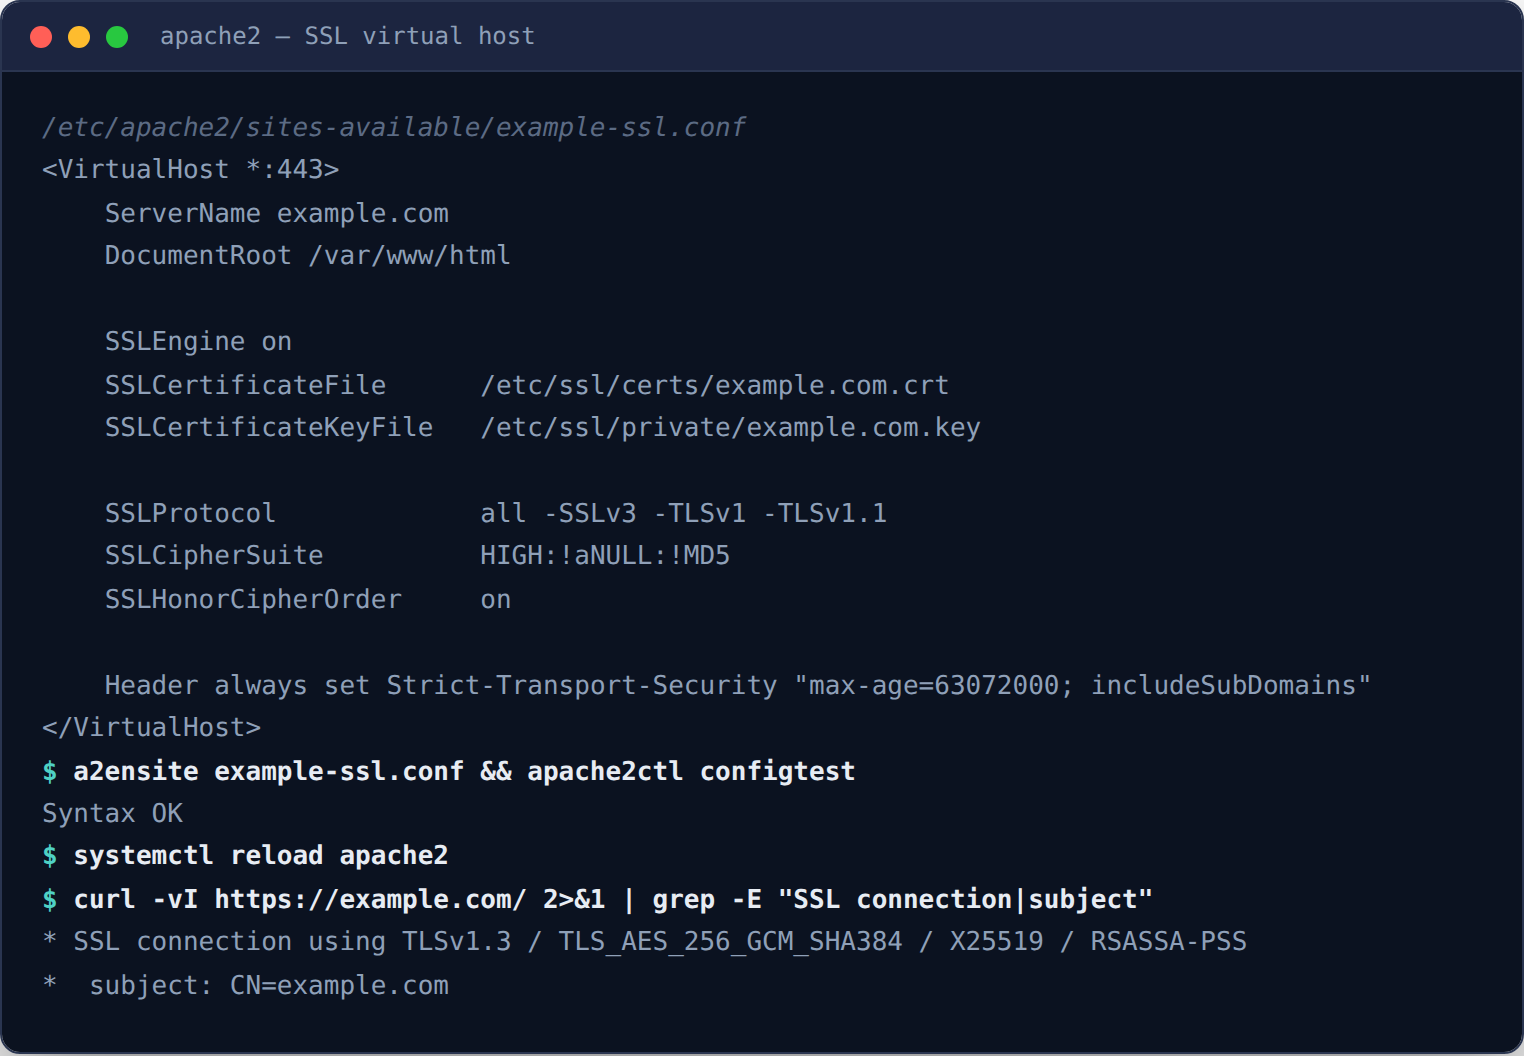
SSLProtocol -all +TLSv1.2 +TLSv1.3
SSLCipherSuite ECDHE-ECDSA-AES128-GCM-SHA256:ECDHE-RSA-AES128-GCM-SHA256:...
SSLHonorCipherOrder off
As with Nginx, use Mozilla's SSL Configuration Generator to produce a current, Apache-specific configuration block rather than assembling the cipher list manually — recommendations shift as cryptanalysis advances, and a generator reflects current guidance rather than a snapshot from whenever a given tutorial was written.
Restart, don't just reload
Some Apache SSL configuration changes require a full restart rather than a graceful reload to take effect fully, depending on your specific module and OS — check your platform's documentation, since a reload that appears to succeed can occasionally leave old settings partially active until a true restart.
mod_ssl versus an alternative TLS module
Most Apache installs handle TLS through mod_ssl, which is OpenSSL-backed and uses the directive syntax above. A minority run mod_gnutls instead, with a completely different, incompatible directive set — run apachectl -M | grep ssl first to confirm which module is actually loaded before assuming SSLCipherSuite applies to your install.
Pinning TLS 1.3 key-exchange groups
Apache 2.4.53 and later also let you constrain which TLS 1.3 key-exchange groups are offered, via SSLOpenSSLConfCmd Groups X25519:P-256 — useful if you need to drop a group Mozilla's generator doesn't exclude by default for your chosen compatibility tier.
Validate the config before reloading, not after
Run apachectl configtest (or httpd -t) before every reload. A typo in the cipher suite list fails silently on some builds instead of refusing to reload — the old configuration stays quietly active, and you won't notice until a scan shows outdated settings still being served.
One included file, many virtual hosts
Put the hardened TLS directives in a single file and pull it into every VirtualHost block with Include /path/to/tls-hardening.conf. A future update to your standard then happens once, not once per vhost — and a scan that still shows an old cipher list on one domain almost always means that vhost never got the Include line added.
Loading comments…